A ransomware incident rarely stays confined to the first computer it reaches. When every workstation, server, printer, camera, and remote connection can communicate freely, a single compromised password can become a company-wide outage. The best practices for network segmentation help contain that damage by placing meaningful boundaries around the systems your business depends on.
For a small or midsize business, segmentation is not about making the network complicated for its own sake. It is about deciding which systems genuinely need to communicate, blocking unnecessary paths, and making it harder for an attacker or malware to move from a front-desk PC to accounting files, a medical records server, or a production system.
What Network Segmentation Should Accomplish
Network segmentation divides a larger network into smaller, controlled areas. These areas may be separated through VLANs, subnets, firewall rules, access control lists, or physical network design. The technology matters, but the business purpose comes first: reduce the blast radius of an incident while keeping staff productive.
A properly segmented network can prevent a guest on Wi-Fi from reaching internal devices. It can keep an infected employee laptop from directly accessing a backup repository. It can also isolate payment terminals, security cameras, building controls, and voice systems from general office traffic.
Segmentation is particularly valuable for organizations handling regulated or sensitive information. A CPA firm may need to separate tax and client-document systems. A medical or dental office may need tighter controls around devices and applications that process protected health information. Municipal offices, legal firms, and hospitality businesses all have different risks, but they share the need to prevent broad, unchecked access across the network.
Start With a Network Inventory, Not a VLAN List
The most common segmentation mistake is creating VLANs before understanding what is connected. A network diagram from five years ago is not enough. Businesses change, add cloud applications, install new wireless access points, and connect devices that are easy to overlook.
Begin by identifying the devices, users, systems, and data flows that matter. This includes workstations, servers, network switches, wireless networks, printers, VoIP phones, cameras, door-access controllers, backup appliances, line-of-business applications, and vendor-managed equipment. Record who owns each system, what it does, where it is located, and what it must communicate with to operate.
Then ask a practical question: if this device is compromised, what could it reach? A copier may need access to a print server and approved email relay service. It usually does not need access to every employee workstation or a financial database. A camera recorder may need to communicate with cameras and authorized viewing stations, but not with payroll files.
This discovery work often identifies risks that are more urgent than the segmentation project itself, such as unsupported operating systems, shared administrator passwords, unknown wireless networks, or firewall rules that allow far more access than intended.
Build Segments Around Risk and Function
The best practices for network segmentation focus on logical business groups rather than arbitrary technical categories. Separate systems when they have different trust levels, different security requirements, or no legitimate reason to communicate directly.
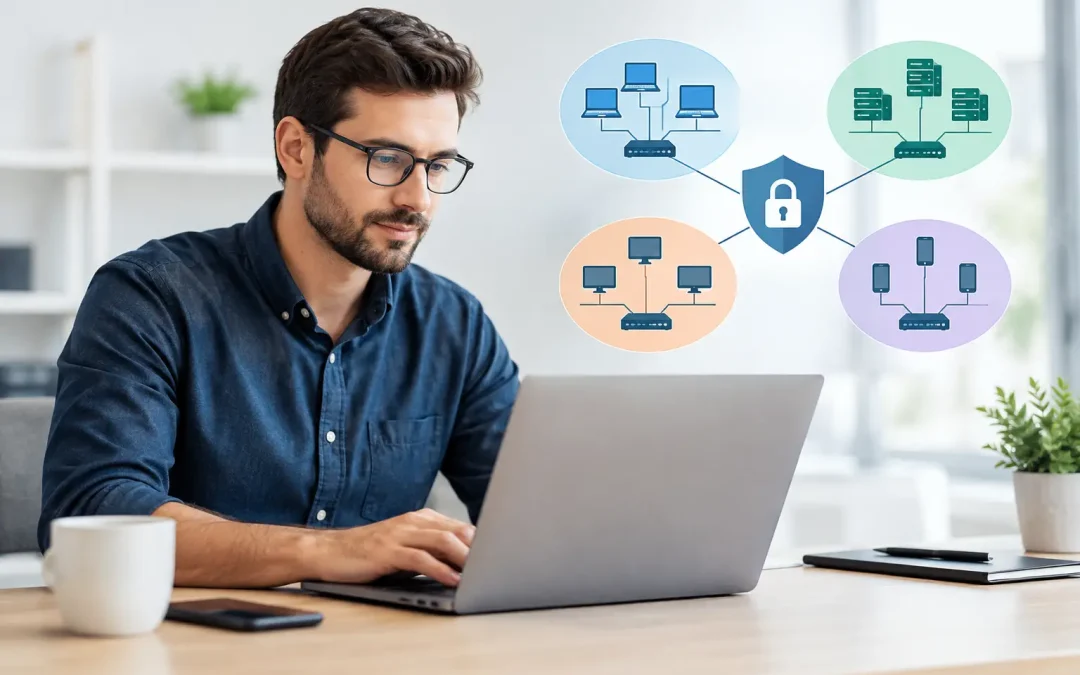
For many businesses, a practical design includes a corporate user network, a server network, a dedicated management network for infrastructure, a voice network, an internet-of-things network for cameras and building devices, a guest wireless network, and a restricted network for sensitive or regulated systems. A backup environment may also deserve its own protected segment, particularly if ransomware protection is a priority.
Not every organization needs every one of these segments. A 12-person professional office has different needs than a multisite medical practice or a warehouse with scanners, cameras, and industrial equipment. The goal is to create enough separation to reduce risk without creating an environment that is difficult to support.
Keep high-risk and low-trust devices away from critical business systems. Guest Wi-Fi should provide internet access only. Cameras, smart TVs, conference-room devices, and other internet-connected equipment should not share unrestricted access with employee computers. Remote-access connections should land in a controlled area and receive only the access required for the employee or vendor’s work.
Enforce Least Privilege Between Segments
Creating separate networks is only half the job. If firewall rules allow all traffic between them, segmentation exists on paper but provides little real protection.
Use a deny-by-default approach between segments whenever possible. Then allow only the specific traffic that is required. For example, employee workstations may need to reach a file server using defined services, while the file server does not need to initiate connections back to every workstation. A voice network may need access to its phone system and selected internet services, but not to a database server.
Rules should be specific enough to be meaningful. Avoid broad policies such as allowing any internal network to communicate with any other internal network. Where feasible, define source and destination networks, protocols, ports, and the purpose of the rule. Document the business owner for exceptions, especially for vendor access and older line-of-business applications.
There is a trade-off. Overly restrictive rules can interrupt printing, software updates, phone service, or specialized applications. The answer is not to open everything permanently. Test changes during an appropriate maintenance window, validate the required workflow, and add only the access that the application needs.
Protect Administrative Access Separately
Network equipment, servers, firewalls, wireless controllers, and backup systems should not be managed from any ordinary employee computer. Administrative credentials have the power to change security controls, create accounts, disable protections, and expose data. They deserve a higher level of protection.
Use a dedicated management segment or secured administrative workstation for infrastructure management. Limit access to named IT administrators, require multifactor authentication where available, and avoid using shared admin accounts. Administrative interfaces should not be reachable from guest wireless networks, general user segments, or the public internet unless there is a documented, secured reason.
Remote support deserves the same discipline. A VPN alone does not automatically make remote access safe. Users and vendors should connect through approved remote-access tools, use multifactor authentication, and receive access only to the systems they need. Vendor accounts should be reviewed regularly and disabled when support agreements or projects end.
Treat Backups as a Protected Recovery Zone
Backups are often the last line of defense after ransomware or a destructive system failure. If attackers can reach and encrypt the backup server from a compromised workstation, recovery becomes much slower and more expensive.
Place backup infrastructure in a restricted segment and tightly control which systems can connect to it. Production servers may need to send backup data to a repository, but ordinary user devices should not browse or administer that repository. Backup administrators should use separate credentials, and backup systems should not rely solely on the same identity platform that manages everyday user access.
Network segmentation is not a substitute for immutable backups, offsite copies, testing, or endpoint security. It works alongside those controls by reducing the chance that an incident can destroy production data and recovery systems through the same unrestricted network path.
Segment Wireless Networks With the Same Care
Wireless networks are frequently where convenience overrides security. Employees, guests, personal devices, printers, tablets, and conference-room equipment are often placed on one wireless network because it is easy to configure. That creates unnecessary exposure.
At minimum, separate corporate wireless access from guest access. Guest users should be isolated from internal resources and, where appropriate, from one another. Devices that cannot support stronger authentication, such as some scanners or smart devices, should be placed on a dedicated network with restricted paths to the services they require.
For corporate wireless, use strong authentication and encryption rather than a widely shared password whenever the environment supports it. Review access after staff changes, and remove old SSIDs that remain active because someone might still use them.
Monitor, Document, and Test the Design
Segmentation is not a one-time firewall project. New applications, acquisitions, office moves, and vendor changes can introduce paths that weaken the original design. Firewall logs, intrusion alerts, network monitoring, and periodic vulnerability testing help identify unexpected traffic and risky exceptions.
Maintain current diagrams, IP address assignments, VLAN definitions, firewall rules, and an explanation of why each major rule exists. Clear documentation reduces downtime during an outage and prevents future changes from accidentally opening a path that was intentionally closed.
Test the controls from both sides. Verify that users can complete normal work, then verify that a device from a lower-trust segment cannot reach protected systems. Penetration testing and security assessments can reveal lateral movement opportunities that routine support may not expose.
For businesses in the Chicago suburbs, a network assessment can be a practical starting point when the existing environment has grown organically over time. Tomorrow’s Solutions can help identify where devices, firewall policies, remote access, and backup systems need stronger separation before an avoidable incident forces the issue.
The right segmentation plan should make daily work feel ordinary while making an attacker’s next move far more difficult. Start with the systems that would hurt most to lose, restrict access carefully, and keep reviewing the design as the business changes.